Introduction
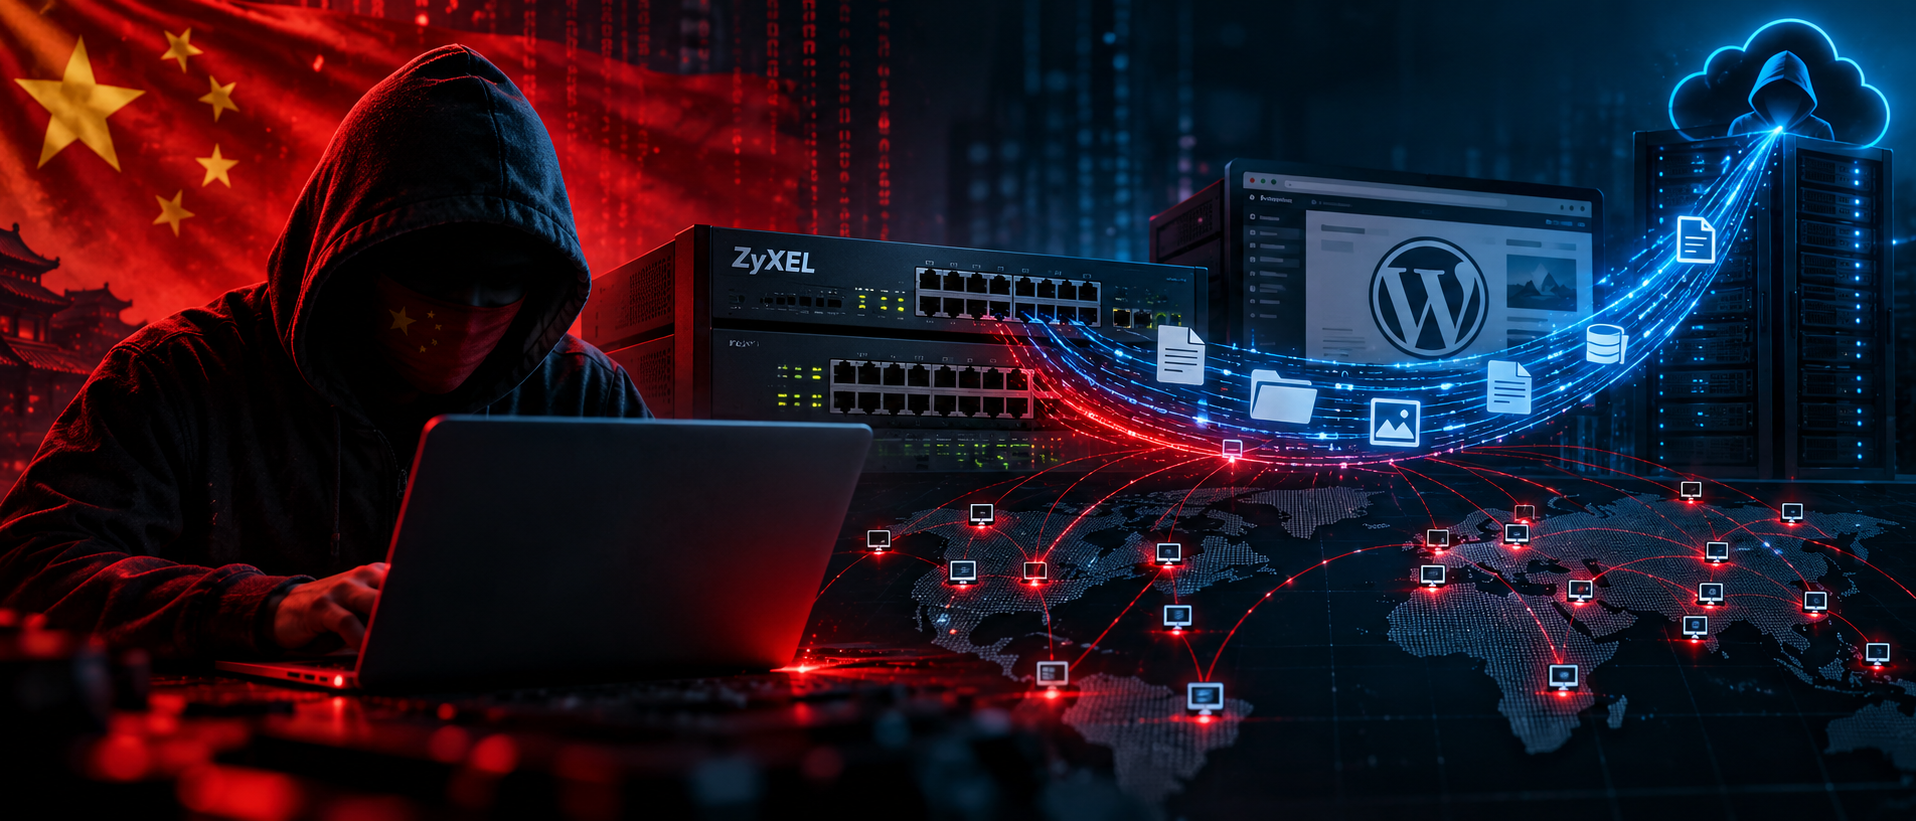
A coordinated campaign targeting both network infrastructure and web platforms has surfaced. The attackers, identified as a Chinese‑speaking threat actor, leveraged separate vulnerabilities in ZyXEL GS1900 Smart Managed Switches and widely deployed WordPress installations. Their activity resulted in the theft of data from 996 devices and the extraction of over 18,500 records stored in backend databases.
What Happened
Confirmed facts indicate that the adversary simultaneously compromised two distinct technology stacks. First, they accessed ZyXEL GS1900 switches, a line of smart managed devices used in enterprise and government networks. Second, they infiltrated WordPress sites, likely exploiting known weaknesses in the content‑management system. The dual‑vector approach allowed the group to move laterally across network segments and harvest data from both hardware and application layers.
Technical Details
While the public disclosure does not enumerate CVE identifiers, the attack pattern suggests a classic blend of firmware‑level exploitation and web‑application compromise.
- ZyXEL GS1900 – The switches run a proprietary firmware stack that historically has accepted unauthenticated configuration commands under certain conditions. An attacker who can inject malicious payloads into the management interface can gain root‑level control, reconfigure ports, and intercept traffic.
- WordPress – The platform’s extensibility makes it a frequent target. Attackers often abuse outdated plugins, insecure themes, or core vulnerabilities to achieve remote code execution. Once a foothold is established, they can pivot to adjacent systems, including network devices that share the same administrative domain.
Both vectors appear to have been leveraged in a coordinated fashion, enabling the threat actor to harvest credentials, capture configuration files, and query backend databases for sensitive records. The scale of the data exfiltration—nearly a thousand devices and tens of thousands of database rows—implies automated tooling rather than manual exploitation.
Who Is Affected
The incident directly impacts organizations that deploy ZyXEL GS1900 Smart Managed Switches and maintain WordPress sites without fully patched software. Government agencies, educational institutions, and private enterprises that rely on these products for internal networking or public‑facing web services are at risk. Any entity with legacy firmware or outdated WordPress components could be exposed to the same exploitation chain.
Why It Matters
Compromise of a managed switch undermines the foundational trust of a network. An attacker with control over switch configuration can:
- Intercept or reroute traffic, exposing credentials and proprietary data.
- Disable security controls, such as VLAN segmentation, creating a broader attack surface.
- Deploy persistent backdoors that survive routine system reboots.
When combined with a compromised WordPress installation, the threat actor gains a two‑pronged view of both external and internal communications. The stolen database records—over 18,500 in total—likely contain personally identifiable information, operational details, or other sensitive data. The breach therefore raises concerns about privacy violations, regulatory non‑compliance, and potential downstream attacks using the harvested intelligence.
Exploitation/Attack Information
The campaign is classified as actively exploited. Threat intelligence feeds have observed repeated attempts to probe ZyXEL devices for the same weakness, and intrusion detection systems have flagged anomalous WordPress login patterns consistent with credential‑stuffing attacks. Indicators of compromise (IOCs) include unusual outbound connections from switch management IPs to external command‑and‑control servers, as well as suspicious PHP files appearing in WordPress plugin directories.
Network traffic analysis shows that the actors favor short‑lived sessions, likely to evade detection. After gaining initial access, they employ internal reconnaissance scripts to enumerate connected hosts, then pivot to the WordPress environment to harvest database dumps. The exfiltration path often leverages encrypted channels, making passive monitoring insufficient without deep packet inspection.
Recommended Actions
Immediate steps are essential to contain the breach and prevent further data loss:
- Patch Firmware: Verify that all ZyXEL GS1900 switches run the latest firmware released by the vendor. Apply any security updates without delay.
- Update WordPress: Ensure the core platform, all plugins, and themes are updated to their current stable versions. Remove any components that are no longer maintained.
- Credential Hygiene: Rotate administrative passwords for both switch management consoles and WordPress accounts. Enforce strong, unique passwords and consider multi‑factor authentication where supported.
- Network Segmentation: Isolate management interfaces on dedicated VLANs with strict ACLs. Limit access to trusted IP ranges and require VPN termination before reaching the devices.
- Log Monitoring: Enable detailed logging on switches and WordPress servers. Correlate logs with a SIEM to detect repeated login failures, configuration changes, or outbound connections to unfamiliar domains.
- Incident Response: Conduct a forensic review of compromised systems. Identify any malicious binaries, scheduled tasks, or altered configuration files, and remove them.
- Backup Verification: Confirm that clean backups exist for both switch configurations and WordPress databases. Test restoration procedures to ensure rapid recovery if needed.
Long‑term measures include establishing a regular patch management cadence, performing periodic vulnerability scans on network devices, and employing a web‑application firewall (WAF) to harden WordPress deployments.
Conclusion
The dual exploitation of ZyXEL GS1900 Smart Managed Switches and WordPress underscores the danger of treating network hardware and web applications as separate security domains. A threat actor fluent in both firmware manipulation and web‑application attacks can harvest data at scale, as evidenced by the theft of records from nearly a thousand devices and more than 18,500 database entries. Organizations must adopt a holistic defense strategy that includes timely patching, strict access controls, and continuous monitoring to thwart similar campaigns.
Sources
- BleepingComputer: https://www.bleepingcomputer.com/news/security/chinese-hackers-exploit-multiple-technologies-to-steal-govt-data/