Introduction
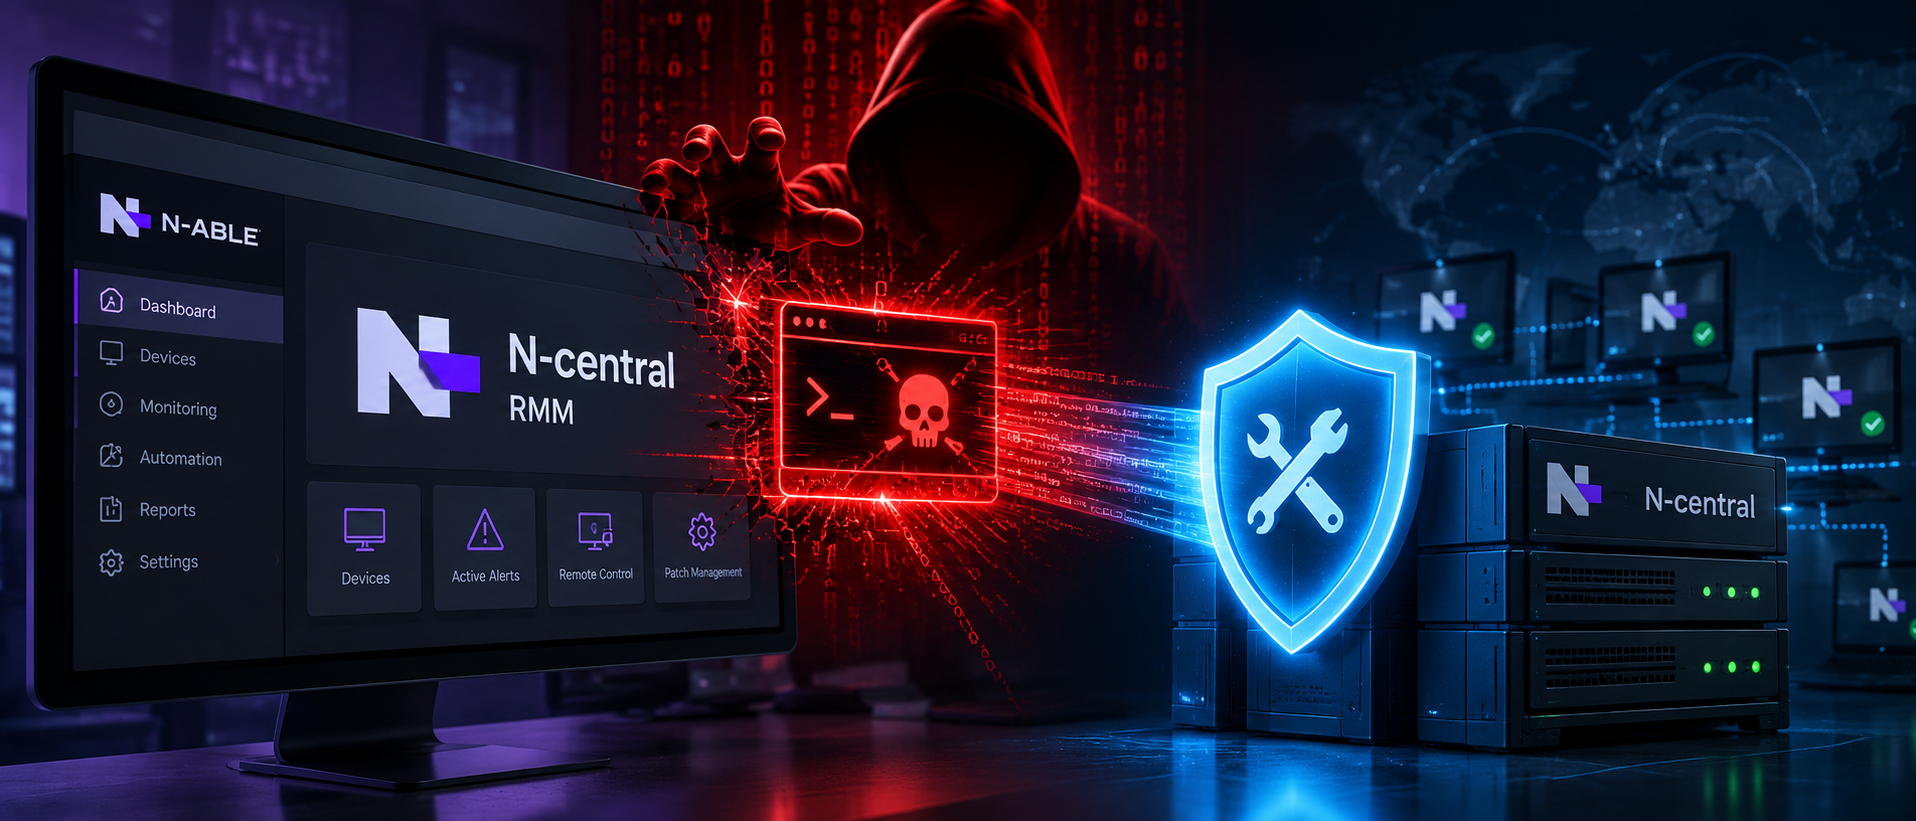
The cybersecurity community received an urgent advisory this week: N-able, a provider of remote monitoring and management (RMM) solutions, rolled out an emergency hotfix for a critical vulnerability in its N‑central platform. The timing of the patch coincides with confirmed attacks leveraging the flaw, underscoring the immediate risk to managed service providers (MSPs) and their clients.
What Happened
N-able disclosed that a maximum‑severity remote code execution (RCE) flaw exists in the N‑central RMM platform. In response, the vendor published an emergency hotfix designed to neutralize the vulnerability. The release came while threat actors were observed exploiting the defect in the wild, prompting the rapid mitigation effort.
Technical Details
The vulnerability permits unauthenticated code execution on affected N‑central installations. While the vendor has not released a CVE identifier or detailed technical specifications, the classification as "maximum severity" indicates a high impact on confidentiality, integrity, and availability. The flaw resides within the core services that enable remote device management, meaning an attacker who successfully exploits it could gain full control over managed endpoints.
Who Is Affected
All organizations that deploy N‑central for remote monitoring and management are potentially exposed. This includes MSPs that manage multiple customer environments, as well as any enterprise that uses N‑central internally. The platform’s widespread adoption in the IT services sector amplifies the scope of impact.
Why It Matters
Remote code execution flaws are among the most dangerous classes of vulnerabilities because they allow attackers to run arbitrary commands on target systems. In the context of an RMM platform, successful exploitation can cascade across dozens or hundreds of managed devices, effectively turning a single breach into a supply‑chain incident. The active exploitation reported by N-able confirms that threat actors are already weaponizing the flaw, raising the urgency for immediate remediation.
Exploitation/Attack Information
Threat actors have been observed targeting the N‑central flaw in real time. Attackers appear to be scanning for vulnerable instances and delivering payloads that execute without user interaction. Because the vulnerability is described as maximum severity, the exploit chain likely requires minimal prerequisites, making it attractive to opportunistic and possibly more sophisticated groups. No specific malware families or attribution have been disclosed, but the ongoing nature of the attacks suggests a coordinated campaign.
Recommended Actions
- Apply the emergency hotfix immediately – N-able’s patch addresses the core weakness; delay increases exposure.
- Validate patch deployment – Use configuration management tools or manual verification to confirm that the hotfix is active on every N‑central instance.
- Conduct a rapid inventory – Identify all systems running N‑central, including legacy deployments that may have been overlooked.
- Monitor network traffic – Look for anomalous connections to N‑central services, especially inbound attempts from unfamiliar IP ranges.
- Enforce least‑privilege access – Restrict administrative credentials for the RMM platform to reduce the blast radius if an account is compromised.
- Review incident response playbooks – Ensure that procedures for RMM‑related compromises are up to date and that relevant stakeholders are alerted.
Conclusion
The emergency hotfix from N-able reflects a critical moment for organizations that rely on the N‑central RMM platform. With the flaw actively exploited, the window for safe operation is closing rapidly. Prompt patching, thorough verification, and heightened monitoring are the only defensible steps to mitigate the risk. Stakeholders should treat this incident as a reminder of the systemic danger posed by vulnerabilities in management infrastructure and adjust their security posture accordingly.
Sources
- BleepingComputer: https://www.bleepingcomputer.com/news/security/n-able-patches-max-severity-n-central-flaw-amid-ongoing-attacks/