Introduction
The geospatial community relies heavily on GeoNetwork, an open‑source catalog that aggregates metadata for maps, datasets, and services. Its widespread adoption across government portals makes any security weakness a potential systemic risk. Recent research uncovered a pair of vulnerabilities that, when combined, enable an attacker to execute code on the server without any authentication. The vendor responded quickly, publishing patches for both the 4.4.x and 4.2.x branches.
What Happened
Security researchers identified two distinct issues within GeoNetwork’s code base. Individually, each flaw presented a limited attack surface, but chaining them bypasses authentication altogether, granting full remote code execution (RCE) capabilities. The vulnerabilities were disclosed publicly on August 31 2026, and the maintainers released corrective versions—4.4.12 and 4.2.17—on July 8 2026, ahead of the public announcement.
Technical Details
Vulnerability 1 – Input Validation Bypass
The first flaw stems from insufficient sanitisation of user‑supplied parameters in the metadata ingestion API. An attacker can inject specially crafted payloads that survive the platform’s validation routine, allowing the server to interpret them as executable commands.
Vulnerability 2 – Deserialization of Untrusted Data
The second issue involves the Java deserialization process used when GeoNetwork processes incoming XML metadata. The component trusts the structure of incoming objects and fails to enforce strict type checks. By delivering a maliciously crafted XML document, an adversary can trigger arbitrary object instantiation.
Exploit Chain
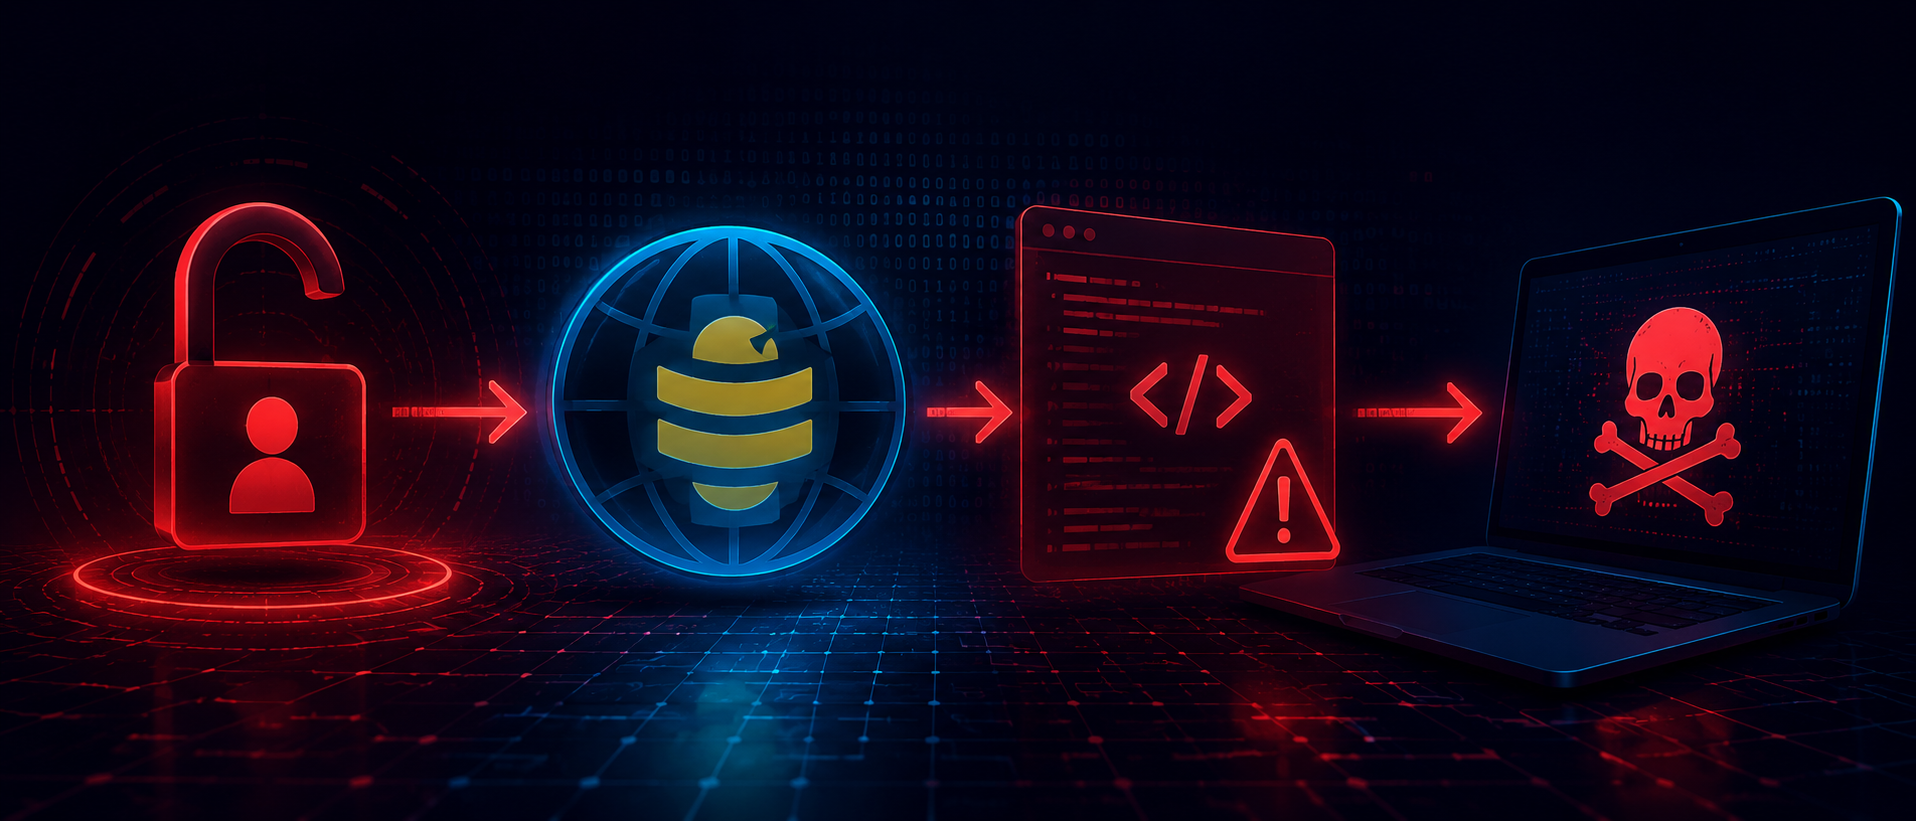
When an unauthenticated actor supplies a malicious request to the ingestion endpoint, the input validation bypass forwards the payload to the deserialization routine. The deserializer then materialises the attacker‑controlled object, which executes system commands under the context of the GeoNetwork service account. Because the chain requires no prior authentication, any reachable instance of the vulnerable platform becomes a viable target.
Patch Overview
The July 8 2026 patches address both weaknesses:
- Input validation: The ingestion API now enforces a whitelist of allowed characters and rejects any payload that deviates from the expected schema.
- Deserialization: The XML parser has been hardened with a secure deserialization library that validates class types against an explicit allow‑list, preventing rogue object creation. Both fixes are back‑ported to the long‑term support 4.2 branch (version 4.2.17) and the newer 4.4 branch (version 4.4.12).
Who Is Affected
Any deployment running a GeoNetwork version earlier than 4.4.12 or 4.2.17 is technically vulnerable. Because the platform underpins many national and regional geoportals, the exposure spans:
- Federal, state, and municipal agencies that expose public metadata catalogs.
- Academic institutions that host research data repositories built on GeoNetwork.
- Private‑sector organisations that embed the catalog as part of location‑based services. The lack of authentication in the exploit chain means that even externally facing instances, which are typically open to the public for metadata search, can be compromised without credential theft.
Why It Matters
Remote code execution remains one of the most severe vulnerability classes. An attacker who gains execution rights on a GeoNetwork server can:
- Manipulate metadata: Altering dataset descriptions, removing provenance information, or injecting malicious links.
- Pivot within the network: The GeoNetwork service often runs with elevated privileges or shares network segments with other critical GIS components, providing a foothold for lateral movement.
- Disrupt public services: Many citizen‑facing portals rely on GeoNetwork for map discovery. Compromise could lead to defacement, data loss, or denial‑of‑service conditions. Given the platform’s role in disseminating geospatial intelligence, any breach could have downstream effects on emergency response, urban planning, and environmental monitoring.
Recommended Actions
- Apply the patches immediately – Upgrade to GeoNetwork 4.4.12 or 4.2.17, depending on the branch in use. Verify the version through the application’s “About” page or by querying the API.
- Validate the upgrade – After installation, run a smoke test that queries the ingestion endpoint with benign data to confirm normal operation.
- Review network exposure – Restrict inbound traffic to the ingestion API to trusted IP ranges where possible. Employ a web‑application firewall (WAF) that can block anomalous XML payloads.
- Monitor for indicators of compromise – Look for unexpected process launches, spikes in CPU usage, or outbound connections from the GeoNetwork host that do not align with normal usage patterns.
- Maintain an inventory – Catalogue all GeoNetwork instances across the organisation, noting version, deployment method (on‑premise, containerised, cloud), and exposure level.
- Plan for future updates – Subscribe to the GeoNetwork mailing list or security advisory feed to receive timely notifications of subsequent patches.
Conclusion
The discovery of a chained, unauthenticated RCE in GeoNetwork underscores the risk inherent in widely deployed open‑source infrastructure. While the vendor’s prompt release of version 4.4.12 and 4.2.17 mitigates the immediate threat, organisations must treat the incident as a reminder to enforce rigorous patch management, limit unnecessary exposure, and continuously monitor for anomalous activity. Prompt remediation will preserve the integrity of geospatial data pipelines that underpin critical public services.
Sources
- The Hacker News: https://thehackernews.com/2026/09/geonetwork-fixes-unauthenticated-rce.html