Introduction
Security teams constantly chase familiar tricks that resurface in new guises. The latest incarnation leverages a fake CAPTCHA dialog to convince victims to download and run malicious software. While the underlying social‑engineering premise mirrors older campaigns, the visual mimicry of a web security control raises the bar for unsuspecting users.
What Happened
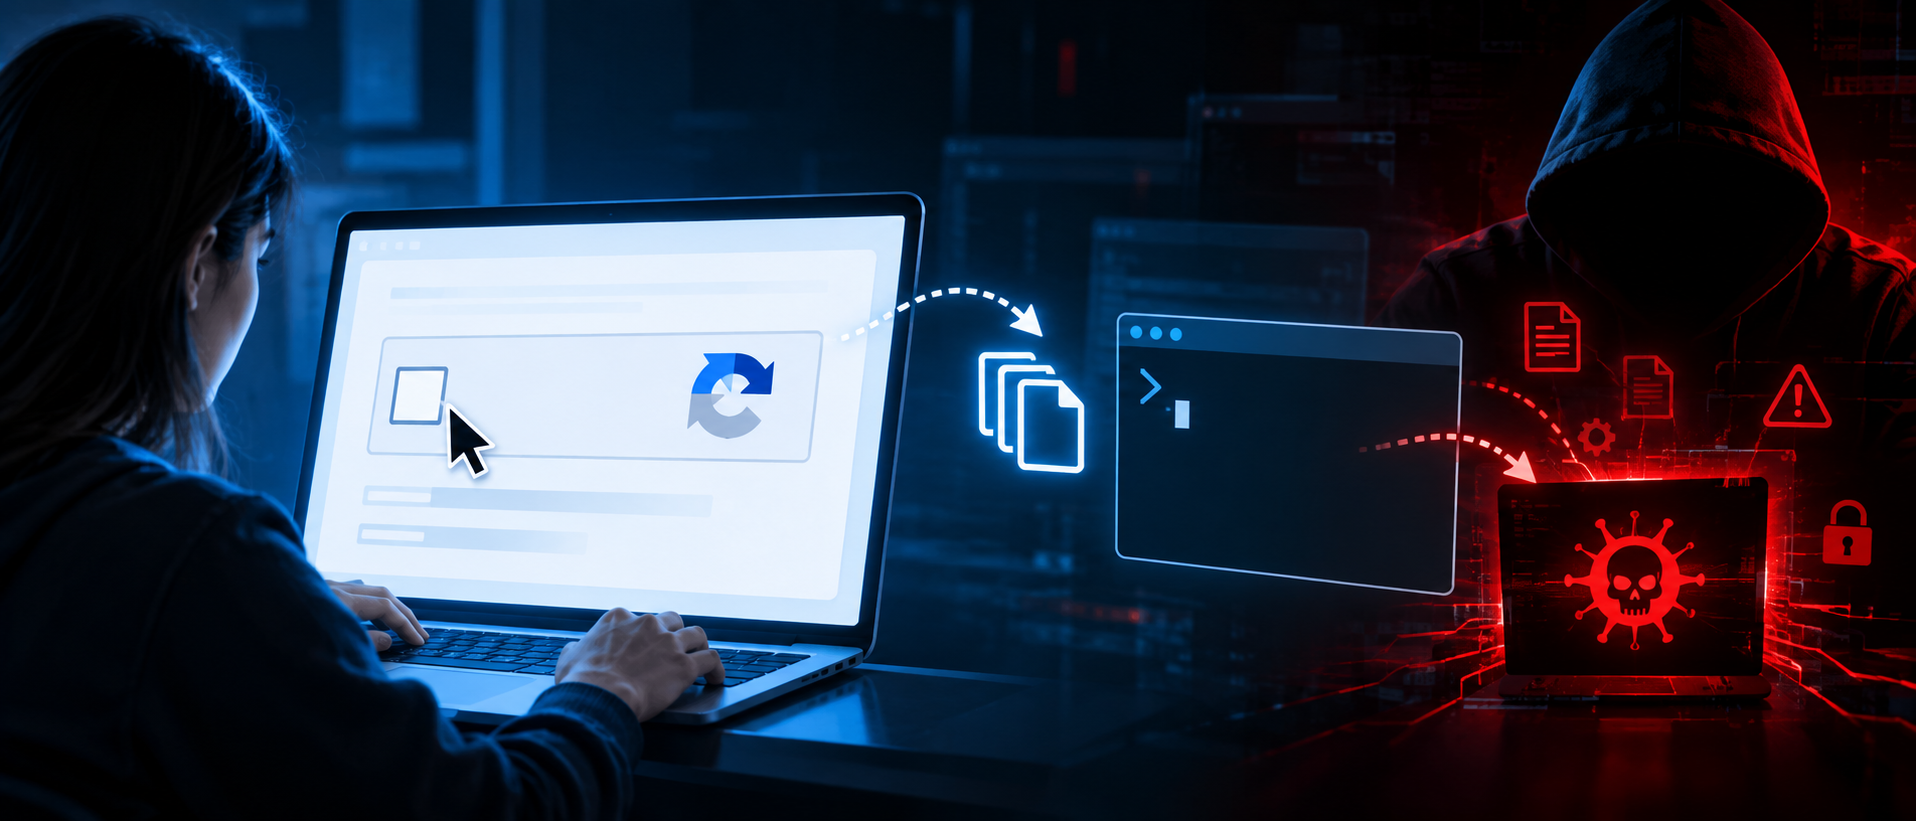
A recent report describes a scam that presents a seemingly ordinary CAPTCHA challenge—those distorted text or image puzzles used to verify human activity. Instead of a legitimate verification, the dialog includes a button or link that, when clicked, initiates the download of an executable file. The user is led to believe that completing the CAPTCHA will grant access to the requested content, but the downloaded program is designed to execute malicious payloads on the host system.
Technical Details
The attack chain follows a straightforward sequence:
- Delivery Vector – The victim encounters a web page that appears authentic, often through a compromised legitimate site or a phishing email containing a malicious link.
- Fake CAPTCHA Rendering – JavaScript or embedded HTML renders a CAPTCHA‑style box that looks identical to common services (e.g., reCAPTCHA). The visual elements—distorted characters, checkbox, or image grid—are replicated using static assets.
- Malicious Action Prompt – Within the fake box, a call‑to‑action such as “Verify” or “Submit” is wired to a download URL rather than a verification endpoint.
- File Retrieval – Clicking the button triggers an HTTP GET request to a server under the attacker’s control. The server responds with a binary executable (often a Windows PE file) masquerading as a harmless utility.
- Execution – The user, believing the download is part of the verification process, runs the file. Once executed, the program may install a backdoor, drop ransomware, or perform credential theft, depending on the attacker’s objective.
The scam does not rely on a zero‑day vulnerability; instead, it exploits user trust in familiar UI patterns. No CVE identifiers are associated with the technique because it does not target software flaws but human perception.
Who Is Affected
Because the lure depends on a generic web interaction, any individual who browses the internet or opens links from untrusted sources is a potential target. Organizations with large employee bases that regularly access external portals—such as SaaS dashboards, vendor portals, or public‑facing services—face heightened exposure. Remote workers, who often use personal devices for work tasks, are especially vulnerable when security controls are less stringent.
Why It Matters
The deceptive use of a CAPTCHA interface blurs the line between security controls and attack vectors. Users have been conditioned to comply with CAPTCHA prompts without question, assuming they are mandatory for site access. By hijacking that expectation, attackers increase their success rate while reducing the need for sophisticated exploit development.
From an operational perspective, the malware delivered through this method can bypass traditional perimeter defenses if the executable is signed with a legitimate certificate or obfuscated to avoid signature‑based detection. Once on the endpoint, the payload can establish persistence, exfiltrate data, or spread laterally across the network.
The broader implication is a reminder that visual spoofing can be as dangerous as code‑level vulnerabilities. Security awareness programs that focus solely on phishing links may miss this nuanced threat.
Recommended Actions
- Update User Training – Incorporate examples of fake CAPTCHA dialogs into regular security awareness curricula. Emphasize that legitimate CAPTCHAs never require a file download.
- Enforce Application Control – Deploy endpoint protection that restricts execution of unsigned or unknown binaries, especially those launched from web browsers.
- Validate Web Content – Use web filtering solutions that inspect page elements for known spoofed UI patterns. Flag pages that embed CAPTCHA‑like widgets from untrusted domains.
- Monitor Network Traffic – Look for anomalous GET requests to rarely accessed domains that deliver executable payloads. Correlate with user activity logs to identify potential compromise.
- Apply Least‑Privilege Principles – Ensure users operate with standard accounts rather than administrative rights, limiting the impact of any inadvertently executed malware.
- Patch Browser Components – Keep browsers and plug‑ins up to date to benefit from built‑in anti‑phishing and download‑blocking features.
Implementing these steps reduces the attack surface and equips users to recognize the visual cues of a counterfeit CAPTCHA.
Conclusion
The emergence of a fake CAPTCHA scam underscores how attackers continuously recycle familiar mechanisms in novel ways. By masquerading as a routine security check, the scheme sidesteps many technical defenses and leans on human complacency. Organizations must adapt both their technical controls and user‑education programs to address this blend of UI spoofing and malicious payload delivery. Vigilance, combined with layered protection, remains the most effective countermeasure.
Sources
- Schneier on Security: https://www.schneier.com/blog/archives/2026/09/fake-captcha-scams.html